What each trust boundary establishes
This figure documents the historical i386 source baseline. Current native x86-64/AArch64 qualification is recorded separately; this is not an ELF64 or native SMP implementation diagram.
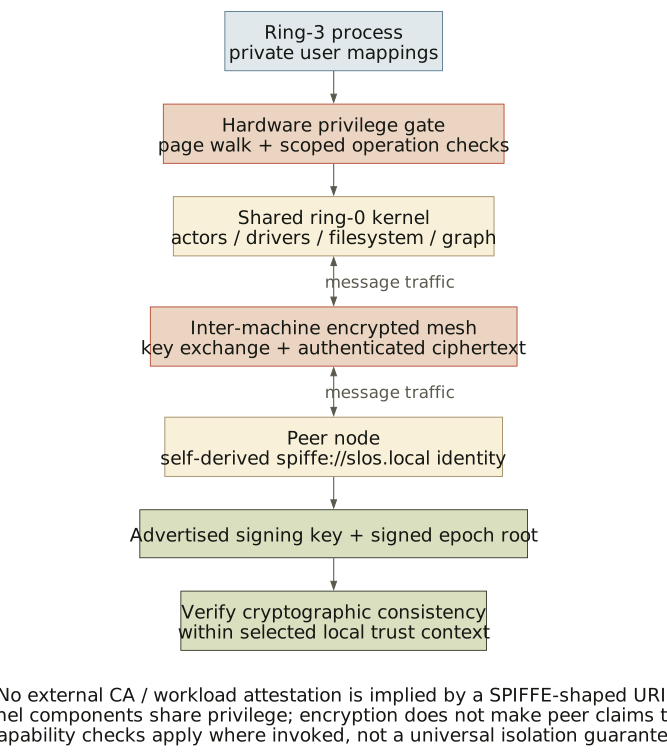
Page isolation, encrypted transport and signed evidence establish different, limited claims.
Text equivalent and source references
- User mappings and the syscall gate separate user processes from kernel privilege. Kernel components themselves share ring 0.
- Mesh encryption authenticates channel traffic under exchanged keys. A self-derived SPIFFE-shaped identity and advertised signing key are not external workload certification.
- Signed roots establish cryptographic consistency with a selected key, not the truth of peer claims. Capability checks only enforce operations at actual check sites.
Trust-flow map. Source paths refer to the atlas baseline; the kernel checkout is private.
include/memory.h · user pointer validationinclude/cap.h · cap_requirekernel/graph/mesh.c · compute_spiffe_id, handle_handshakekernel/graph/federation.c · signing-key / epoch-root handling